Edge & WAAP
Is hostile traffic stopped before it reaches your applications?
- WAF / WAAP coverage and blocking mode
- Bot and abuse controls
- DDoS readiness
- Origin exposure and bypass paths
You getCoverage map and a safe path from monitoring to blocking.
Available for assessments · Colombo + remote
Application Security Consultant
I assess how well your web, API and mobile applications are protected, show you exactly where the gaps are, and give you a prioritised plan to close them.

01 / How I work
I am a consultant, not a reseller. Nothing gets deployed by default: we start by measuring what you have, then decide together what is worth doing and who should do it.
I audit your applications and the security capabilities you already have: edge, APIs, code, monitoring, mobile and governance. Evidence, not questionnaires.
You get a prioritised plan: what to fix first, what it costs, what risk it removes, and what can wait.
If you want help delivering, I scope it case by case: the expertise and manpower it needs, the timeline, and who is best placed to do it — your team, a partner or Innov8’s AppSec unit.
02 / What I assess
Every assessment covers the same six areas, so your results are comparable year on year and across business units.
Score yourself on all six nowIs hostile traffic stopped before it reaches your applications?
You getCoverage map and a safe path from monitoring to blocking.
Do you know every API you expose, and who can call it?
You getComplete API inventory with the risky endpoints ranked.
Are you fixing the weaknesses an attacker would actually use?
You getA prioritisation model your teams can work from every week.
Would your SOC see an application attack while it is happening?
You getTelemetry gaps closed and detections tied to real attack paths.
Can your customer app defend itself on a device you do not control?
You getMobile threat model and a protection policy that respects UX.
Is application security owned, measured and funded?
You getA scored baseline and a 12–24 month roadmap the board can fund.
03 / Engagements
Pick the format that matches the decision you face. Not sure which? The first call is free and that is exactly what it is for.
| Engagement | You get | Duration | Fee | Enquire |
|---|---|---|---|---|
| AppSec maturity assessment | Scored baseline, gap analysis, 12–24 month roadmap, board summary | 2–3 weeks | Fixed fee | Enquire |
| Application architecture review | Threat model, control coverage map, prioritised fixes | 1–3 weeks | Fixed fee | Enquire |
| WAAP & API protection assessment | Coverage gaps, bypass paths, migration or tuning plan | 2–4 weeks | Fixed fee | Enquire |
| Mobile app security assessment | Mobile threat model, protection policy, MASVS test plan | 1–2 weeks | Fixed fee | Enquire |
| Exposure management (CTEM) assessment | Prioritisation model, validation approach, owner playbook, metrics | 2–4 weeks | Fixed fee | Enquire |
| Executive briefing or team workshop | Plain-language risk briefing or hands-on workshop | ½–1 day | Fixed fee | Enquire |
| Fractional AppSec advisor | Roadmap governance, vendor and design reviews, escalation support | Monthly | Retainer | Enquire |
04 / Track record
Hands-on programmes I have led. Client names are withheld under NDA; tap a redacted word to see why.
Banking · A leading Sri Lankan private bank
Moved roughly 112 web applications and APIs to cloud web application and API protection in waves, from monitoring to blocking.
Manufacturing · A global apparel group headquartered in Sri Lanka
Deployed web application, API and advanced bot protection across around 120 applications for a multinational manufacturing group.
Banking · A Tier-1 Sri Lankan commercial bank
Upgraded the vulnerability management platform and deployed web application scanning to cover the application layer.
Banking · A leading private bank’s mobile app
Rolled out in-app protection for a customer banking app, tuning policies and supporting SDK integration with the bank’s developers.
Banking · A leading Sri Lankan private bank
Integrated WAAP security logs into the bank’s SIEM through Logstash and resolved pipeline backpressure so events arrive reliably.
05 / Where I work
When a recommendation needs licences, implementation or managed services and Innov8 is the right fit, my unit delivers it. It is one option, never the default, and always disclosed.
Innov8 AppSec servicesWAF, WAAP, API security, bot mitigation and CDN, deployed and tuned for production.
Runtime protection, app shielding and mobile security testing.
Vulnerability scanning, SAST, DAST and VAPT.
Security logs, observability and SIEM integrations.
Policy tuning, threat monitoring and ongoing operations.
Platform licences, renewals and certified engineering support.
Platforms deployed and operated in production
I have spent my career inside application security programmes, not beside them: migrating more than a hundred production applications to cloud WAAP, rolling out mobile app protection for a bank, modernising vulnerability management and wiring security telemetry into SOCs.
That is why my assessments are practical. I know what happens when a control meets a legacy application, a production deadline and a nervous change board, and I write recommendations your teams can actually deliver.
If a control cannot survive a legacy app, a release deadline and a change board, I will not recommend it.
Product, architecture, configuration or integration: I find which one is actually failing.
Every recommendation comes with cost, effort and the risk it removes.
Advice comes first and stays vendor-neutral. Delivery is your choice.


Free · 12 questions · 3 minutes
Get an instant score across the six areas I assess, and a short report with the next three actions for each.
Cloud WAAP migration lessons from onboarding ~112 applications: DNS cutover order, TLS compatibility, origin protection, staged blocking and SIEM logging.
ReadContinuous threat exposure management (CTEM) for South Asian enterprises: the five stages, better vulnerability prioritisation and how to mobilise owners.
ReadMobile app shielding and RASP for banking apps explained: the threats in-app protection stops, what it cannot replace, and how to tune policy without friction.
ReadA practical OWASP SAMM assessment guide: run a lightweight AppSec maturity assessment in 2–3 weeks, score honestly, set a target and build a security roadmap.
Read08 / FAQ
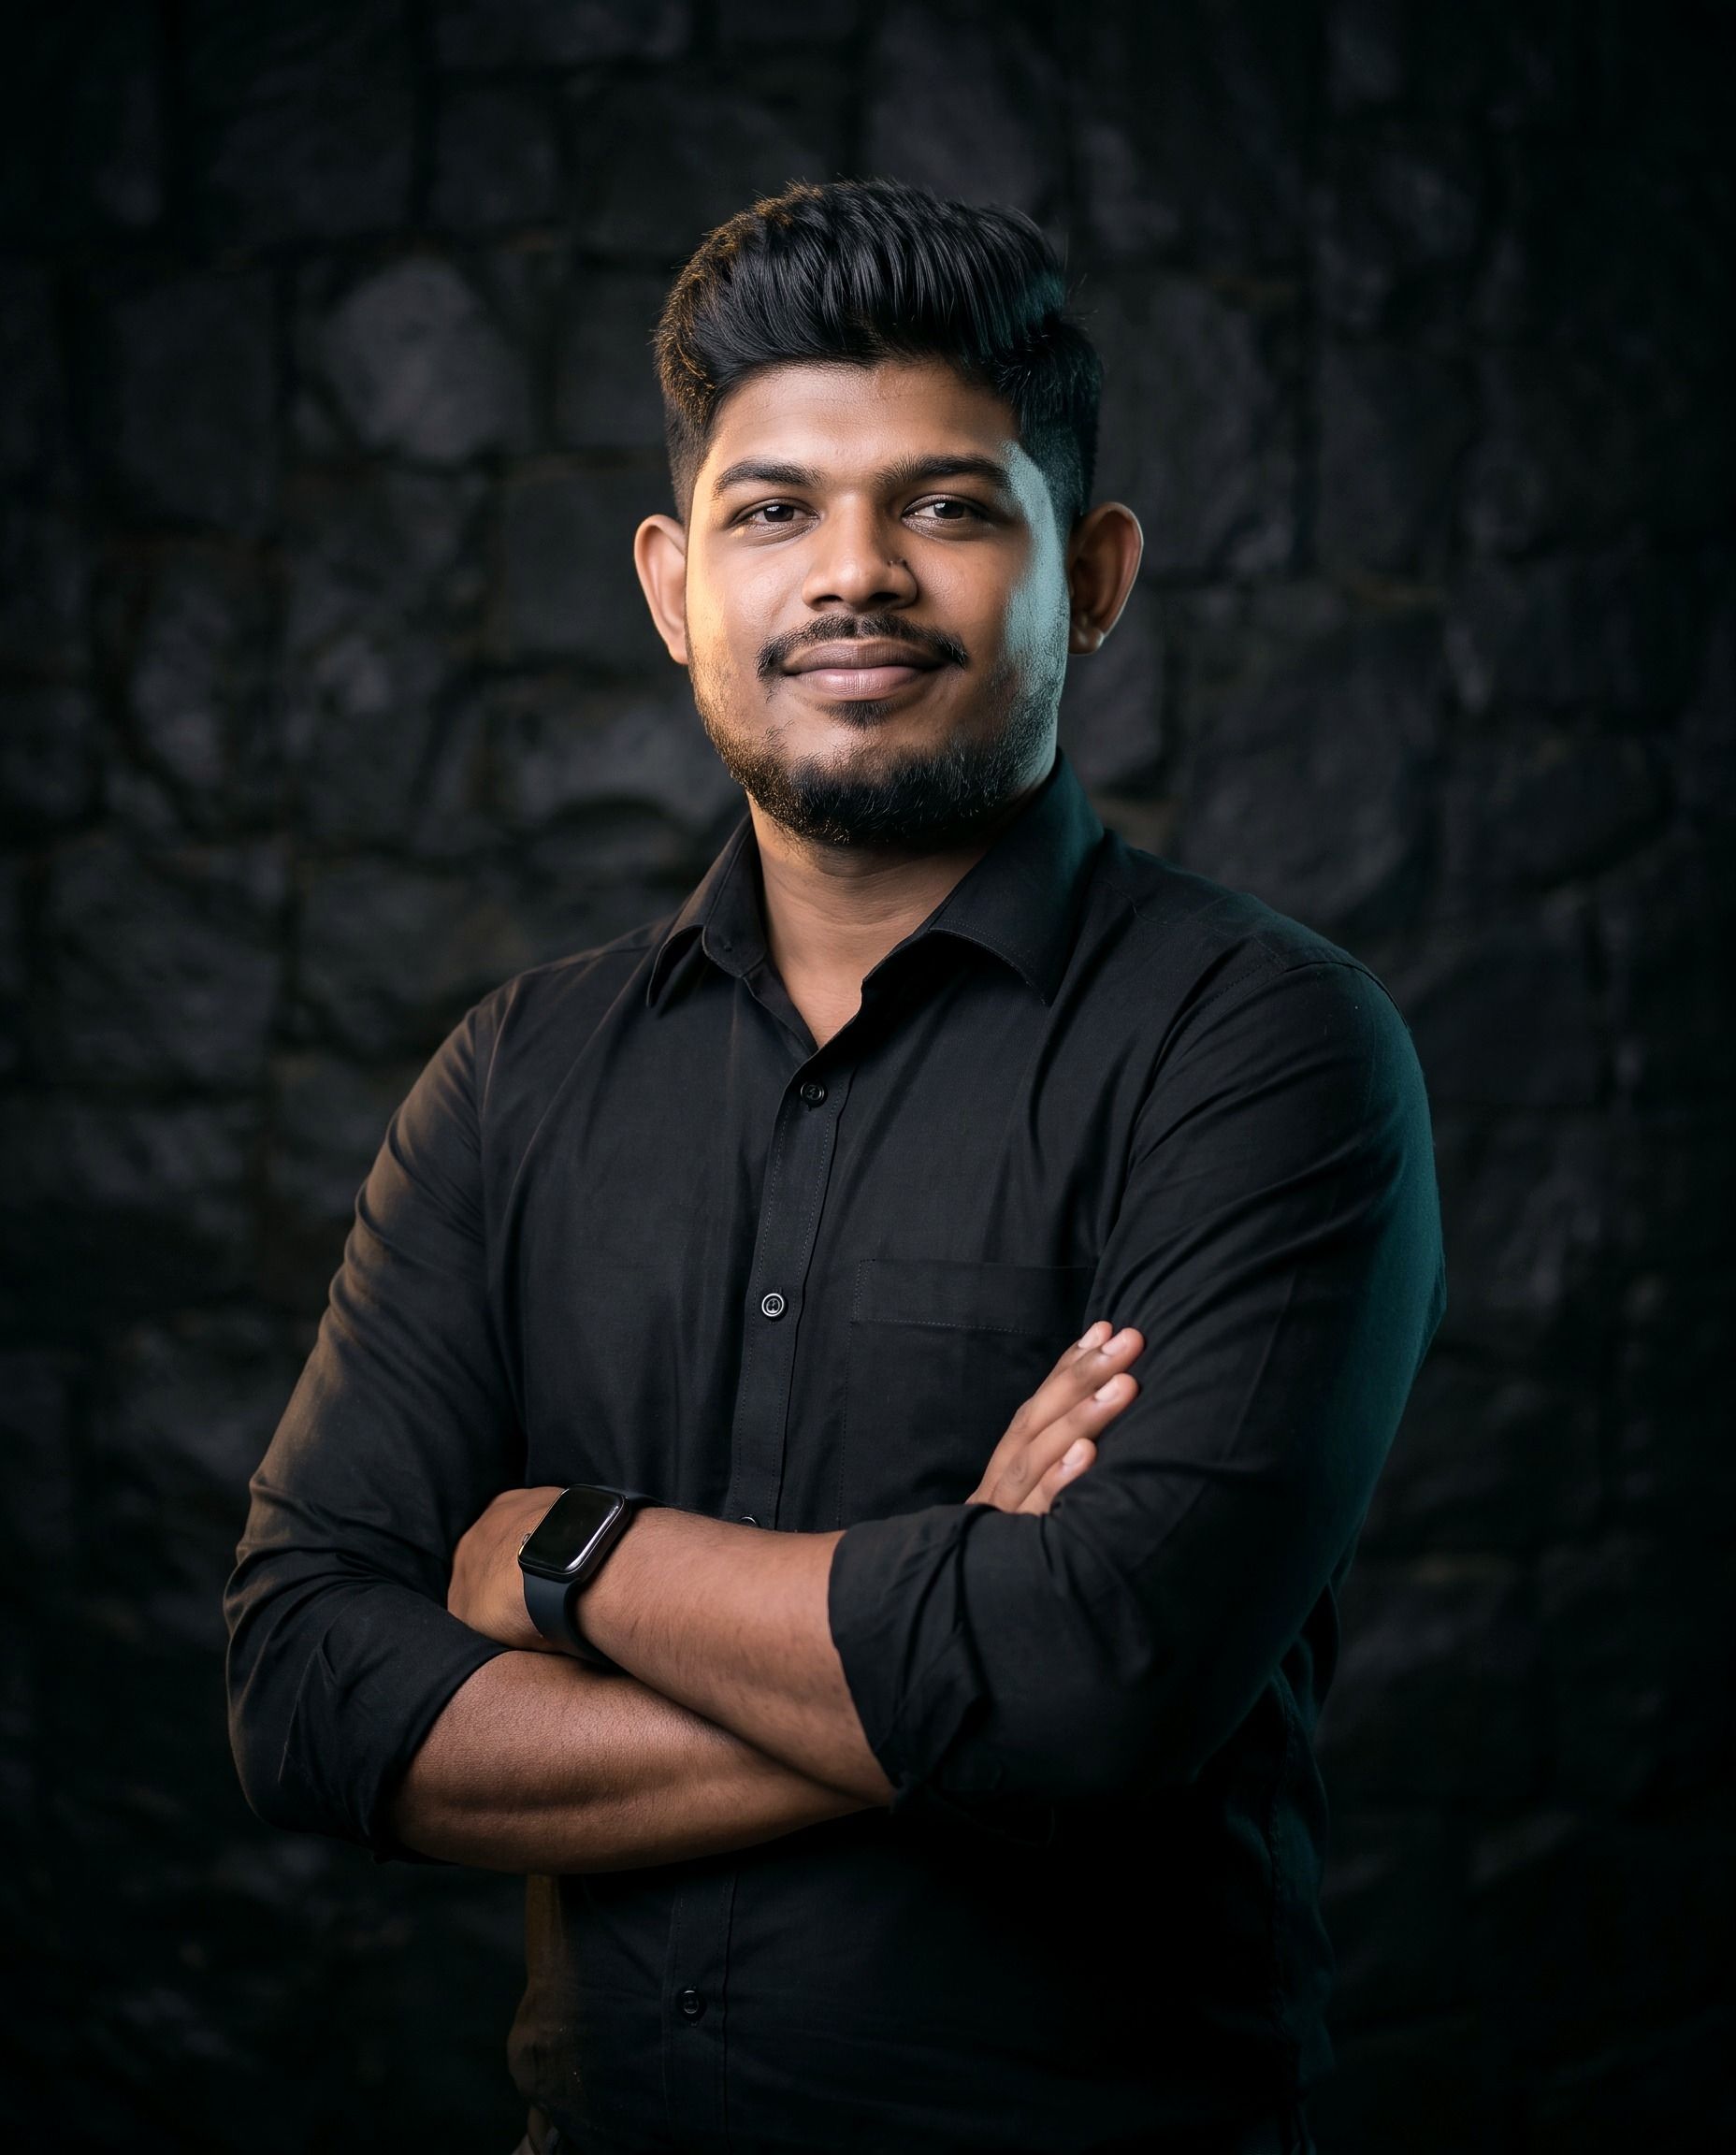
Ravindu Fernando is a Colombo-based Application Security Consultant and head of the Application Security Business Unit at Innov8 (Pvt) Ltd. He assesses web, API, mobile and cloud application security for banks and enterprises and recommends prioritised fixes. He has delivered programmes such as a cloud WAAP migration of around 112 applications for a leading Sri Lankan private bank.
Every engagement starts with an assessment of your applications and existing security capabilities. You then receive prioritised recommendations: what to fix first, what it costs and what risk it removes. Execution is not assumed. If you want help delivering, it is scoped case by case based on the expertise, manpower and timeline required.
Only where it makes sense, and case by case. Your own team, a partner of your choice or Innov8’s Application Security Business Unit can deliver, and I can provide independent oversight. When Innov8 is an option, that relationship is disclosed up front.
Sri Lanka, the Maldives and wider South Asia, the GCC and the Middle East, and remotely across APAC and Australia. Assessments can run remotely or on site in Colombo, with on-site workshops arranged where they add value.
09 / Contact
The first call is free. You will leave it knowing whether an assessment makes sense and what it would cover.