About me
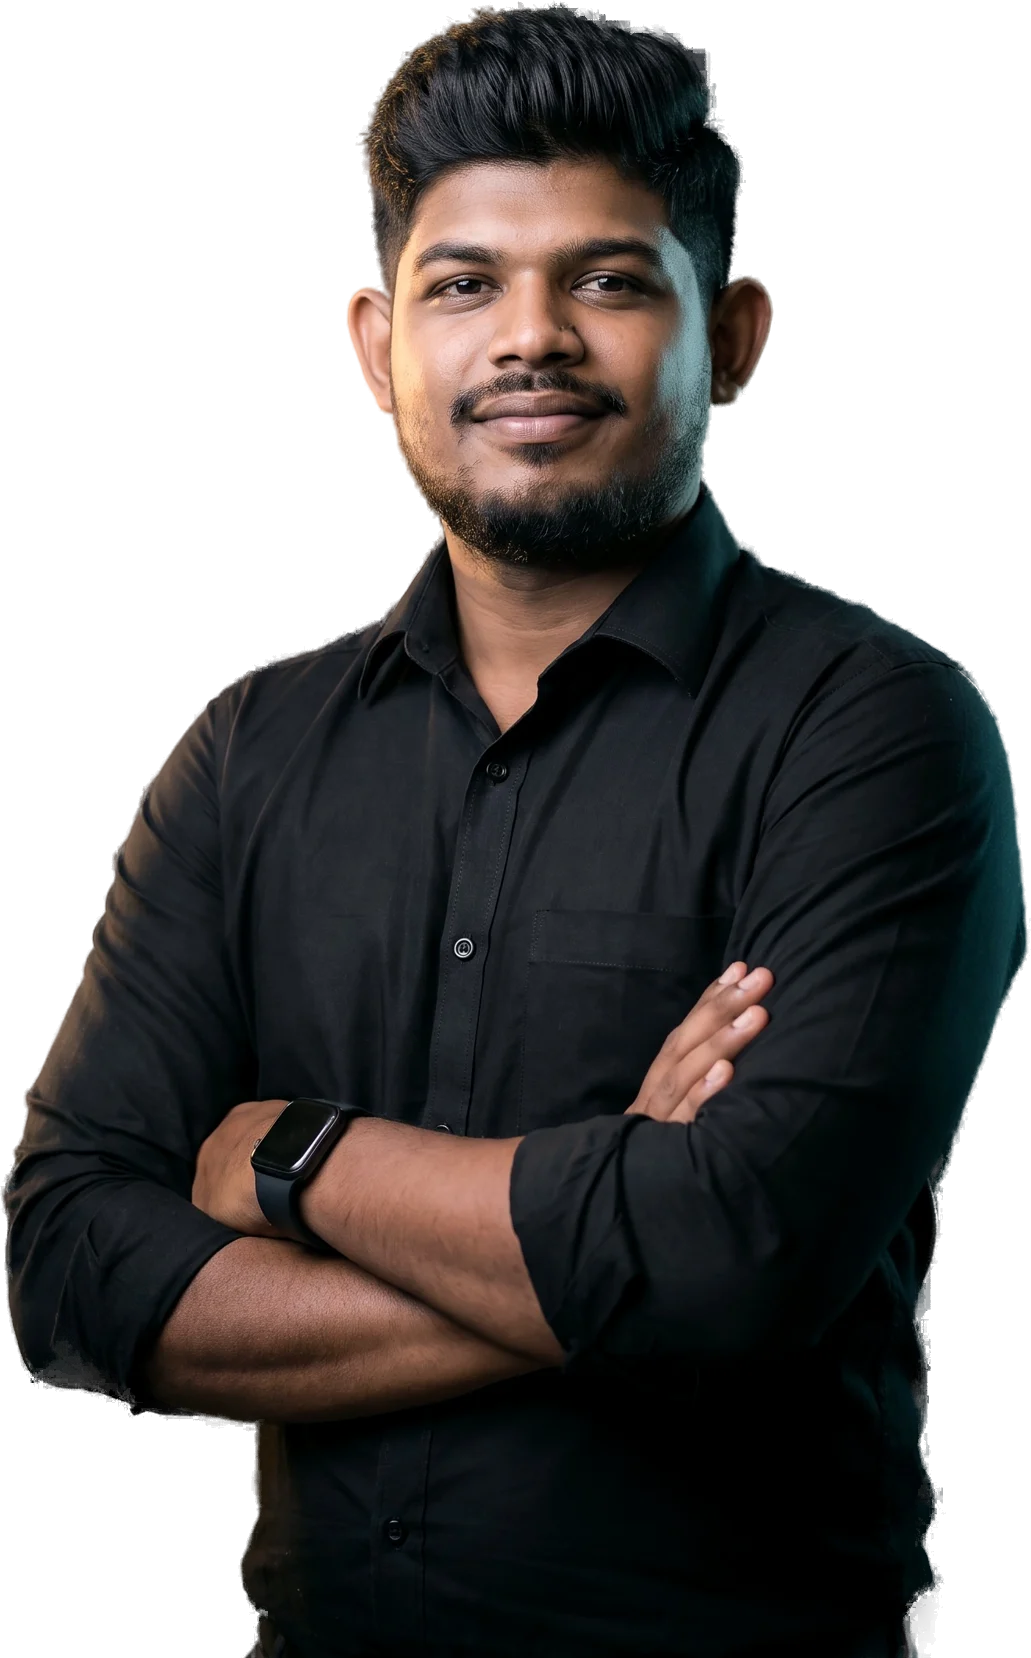
I’m Ravindu. I make application security work in production.
I am a Colombo-based application security consultant. I assess how well your web, API and mobile applications are protected, show you where the gaps are, and give you a plan you can act on. I learned how by delivering it.
- Application Security Consultant
- Head of AppSec BU, Innov8
- Colombo · GMT+5:30
Two roles, fully disclosed
Independent advice. Optional delivery.
You always know which hat I am wearing. Assessment and recommendations are independent; execution is a separate decision you make afterwards.
- Evidence-based assessment of six areas
- Prioritised plan with effort and cost ranges
- Vendor-neutral, fixed fee
- Scoped by expertise, manpower and timeline
- Innov8 AppSec BU, which I head, is one option
- Independent oversight if someone else delivers
How I think
Four things I will not compromise on.
- Evidence, not questionnairesI look at consoles, logs, policies and traffic. A control is only real if it shows up in the evidence.
- Fix order beats fix countA long list of findings helps nobody. The value is in knowing what to fix first, and why.
- Vendor-neutral by defaultRecommendations start from your risk, not a product list. You can take the plan to anyone.
- Production is the testIf a control cannot survive a legacy app, a release deadline and a nervous change board, I will not recommend it.
Work that shaped me
Five programmes, all in production.
- 112Cloud WAAP migration at enterprise scaleF5 Distributed Cloud
- 120WAAP, API security and advanced bot protectionImperva
- T1Vulnerability management modernisationTenable Security Center
- RASPMobile application runtime protectionZimperium
- SIEMWAAP security telemetry into the SOCF5 → Logstash → Trellix SIEM
- NowAssessment-first consultingSri Lanka, South Asia, GCC, APAC
Toolkit
Platforms I have deployed and run.
- F5 Distributed Cloud
- Imperva
- Zimperium
- Veracode
- Tenable
- Qualys
- RidgeBot
- Datadog
- Trellix
- Logstash
Frameworks
Standards I assess against.
- OWASP SAMM v2
- NIST CSF 2.0
- OWASP Top 10
- OWASP API Security Top 10
- OWASP MASVS
- CVSS, EPSS and CISA KEV
- Gartner CTEM
- Education
- degree, university
- Certifications
- to be confirmed
- Experience
- years in cyber security
- Languages
- English
Off the slides
In workshops, at the table, at the keyboard.
Who is Ravindu Fernando?
Ravindu Fernando is a Colombo-based application security consultant and Head of the Application Security Business Unit at Innov8 (Pvt) Ltd. He assesses web, API and mobile application security for banks and enterprises and recommends prioritised fixes, drawing on programmes such as moving around 112 bank applications to cloud web application and API protection (WAAP).
How do your consulting work and your Innov8 role fit together?
Consulting is assessment-first and independent: I measure what you have and recommend what to fix. If you then want help delivering, the work is scoped case by case and can go to your own team, a partner of your choice or Innov8’s Application Security Business Unit, which I head. That relationship is always disclosed up front.
What makes your assessments different?
They come from delivery. I have migrated production applications to cloud WAAP, rolled out mobile app protection for a bank, modernised vulnerability management and fixed SIEM pipelines. That is why my recommendations account for legacy systems, change boards and release deadlines, not just best practice.