Speaking · 6 topics · Keynote, Workshop, Briefing, Panel
Talks from the field, not from the slides of others.
I speak about what I have done in production: moving hundreds of applications to cloud WAAP, shielding banking apps, finding shadow APIs and getting attacks in front of the SOC.
 Keynotes · workshops · briefings
Topics
Pick a topic, or let me tailor one.
Every session is grounded in real programmes, with the client names removed and the lessons left in.
- Keynote30–45 min
The WAF is the easy part: what 230+ applications taught me
Cloud WAAP projects rarely fail on policy. They fail on inventory, DNS order, TLS and open origins. Lessons from onboarding 230+ applications at a bank and a manufacturer.
- Why the inventory, not the WAF policy, is the migration plan
- How to move from monitoring to blocking without outages
- The origin lockdown step that is easiest to leave too late
CISOs and heads of security · Infrastructure and network leaders · Security conference audiences
- Keynote30–45 min
Fix fewer things: exposure management beyond CVSS
A CVSS-sorted list says how severe a flaw is, not what to fix first. How continuous threat exposure management turns scan output into a short list teams can defend.
- Why severity is not risk, and the four kinds of context to add
- The five CTEM stages, and the one where most programmes stall
- Measures that show exposure falling, not just scanning effort
CISOs and security leaders · Vulnerability management and IT operations teams
- WorkshopHalf day
Shadow APIs: finding the endpoints nobody listed
Hands-on: compare the APIs your teams think they publish with what live traffic shows, then rank the risky endpoints against the OWASP API Security Top 10 (2023).
- A repeatable way to reconcile documented and discovered endpoints
- Why broken object level authorisation needs a code fix, not a WAF rule
- A first ranking of your riskiest endpoints to take back to work
Application and API developers · Security engineers and architects · Platform and DevOps teams
- WorkshopHalf day
Shielding a banking app without locking customers out
What RASP and app shielding stop, what they cannot replace, and how to build a response policy that protects customers without flooding the call centre.
- A threat-to-response matrix security and fraud teams can both sign
- A rollout plan from report-only to enforcement
- The server-side controls that must hold if the app is compromised
Mobile development teams · Digital banking and fraud teams · Security architects
- Briefing60–90 min
Application security on one page: a board briefing
Where application risk sits, how to measure maturity with OWASP SAMM v2 and NIST CSF 2.0, and the decisions and budget the board actually needs to make. Plain language, no jargon.
- Current and target maturity by business function, on one page
- How application security fits the NIST CSF 2.0 Govern function
- Three questions to ask management every quarter
Boards and board risk committees · CEOs, CIOs and CISOs
- Panel45–60 min
Can your SOC see an application attack?
SOCs often watch networks and endpoints well but see little inside web apps, APIs and mobile apps. A panel topic on closing that gap, from log pipelines to alert ownership.
- Which WAAP, API and mobile events are worth sending to the SIEM
- Why log pipelines fail on attack days, and how to size them
- Who should own application alerts: SOC, fraud or app teams
SOC managers and analysts · CISOs and security architects · Industry forums and conference panels
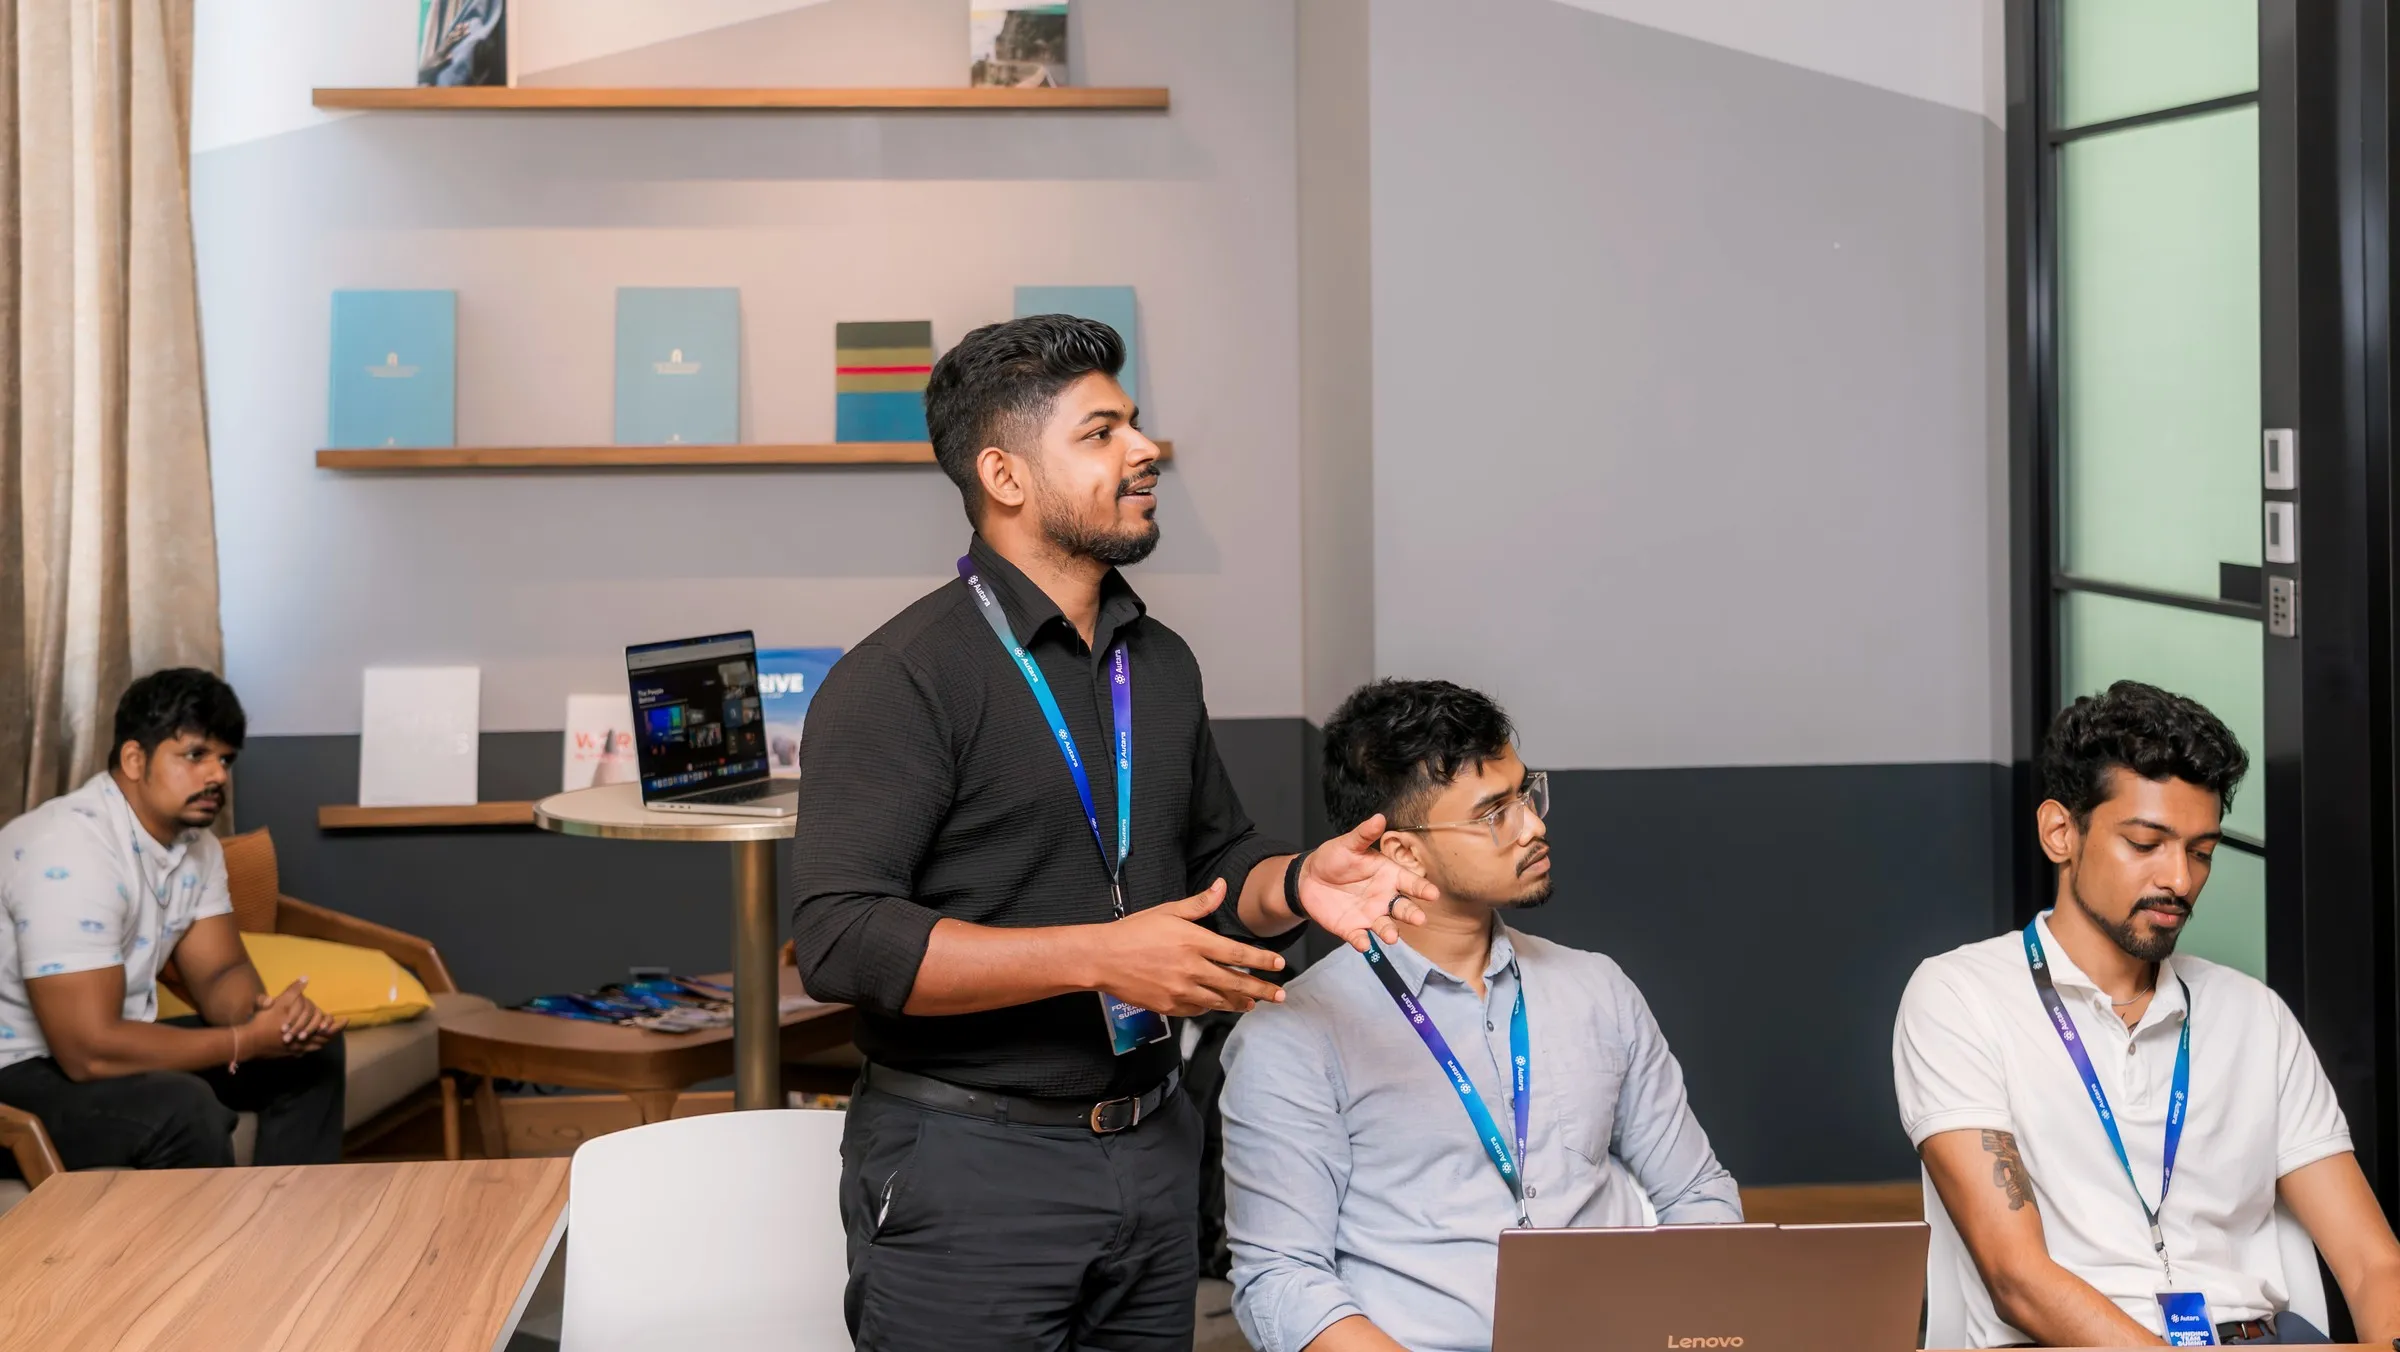
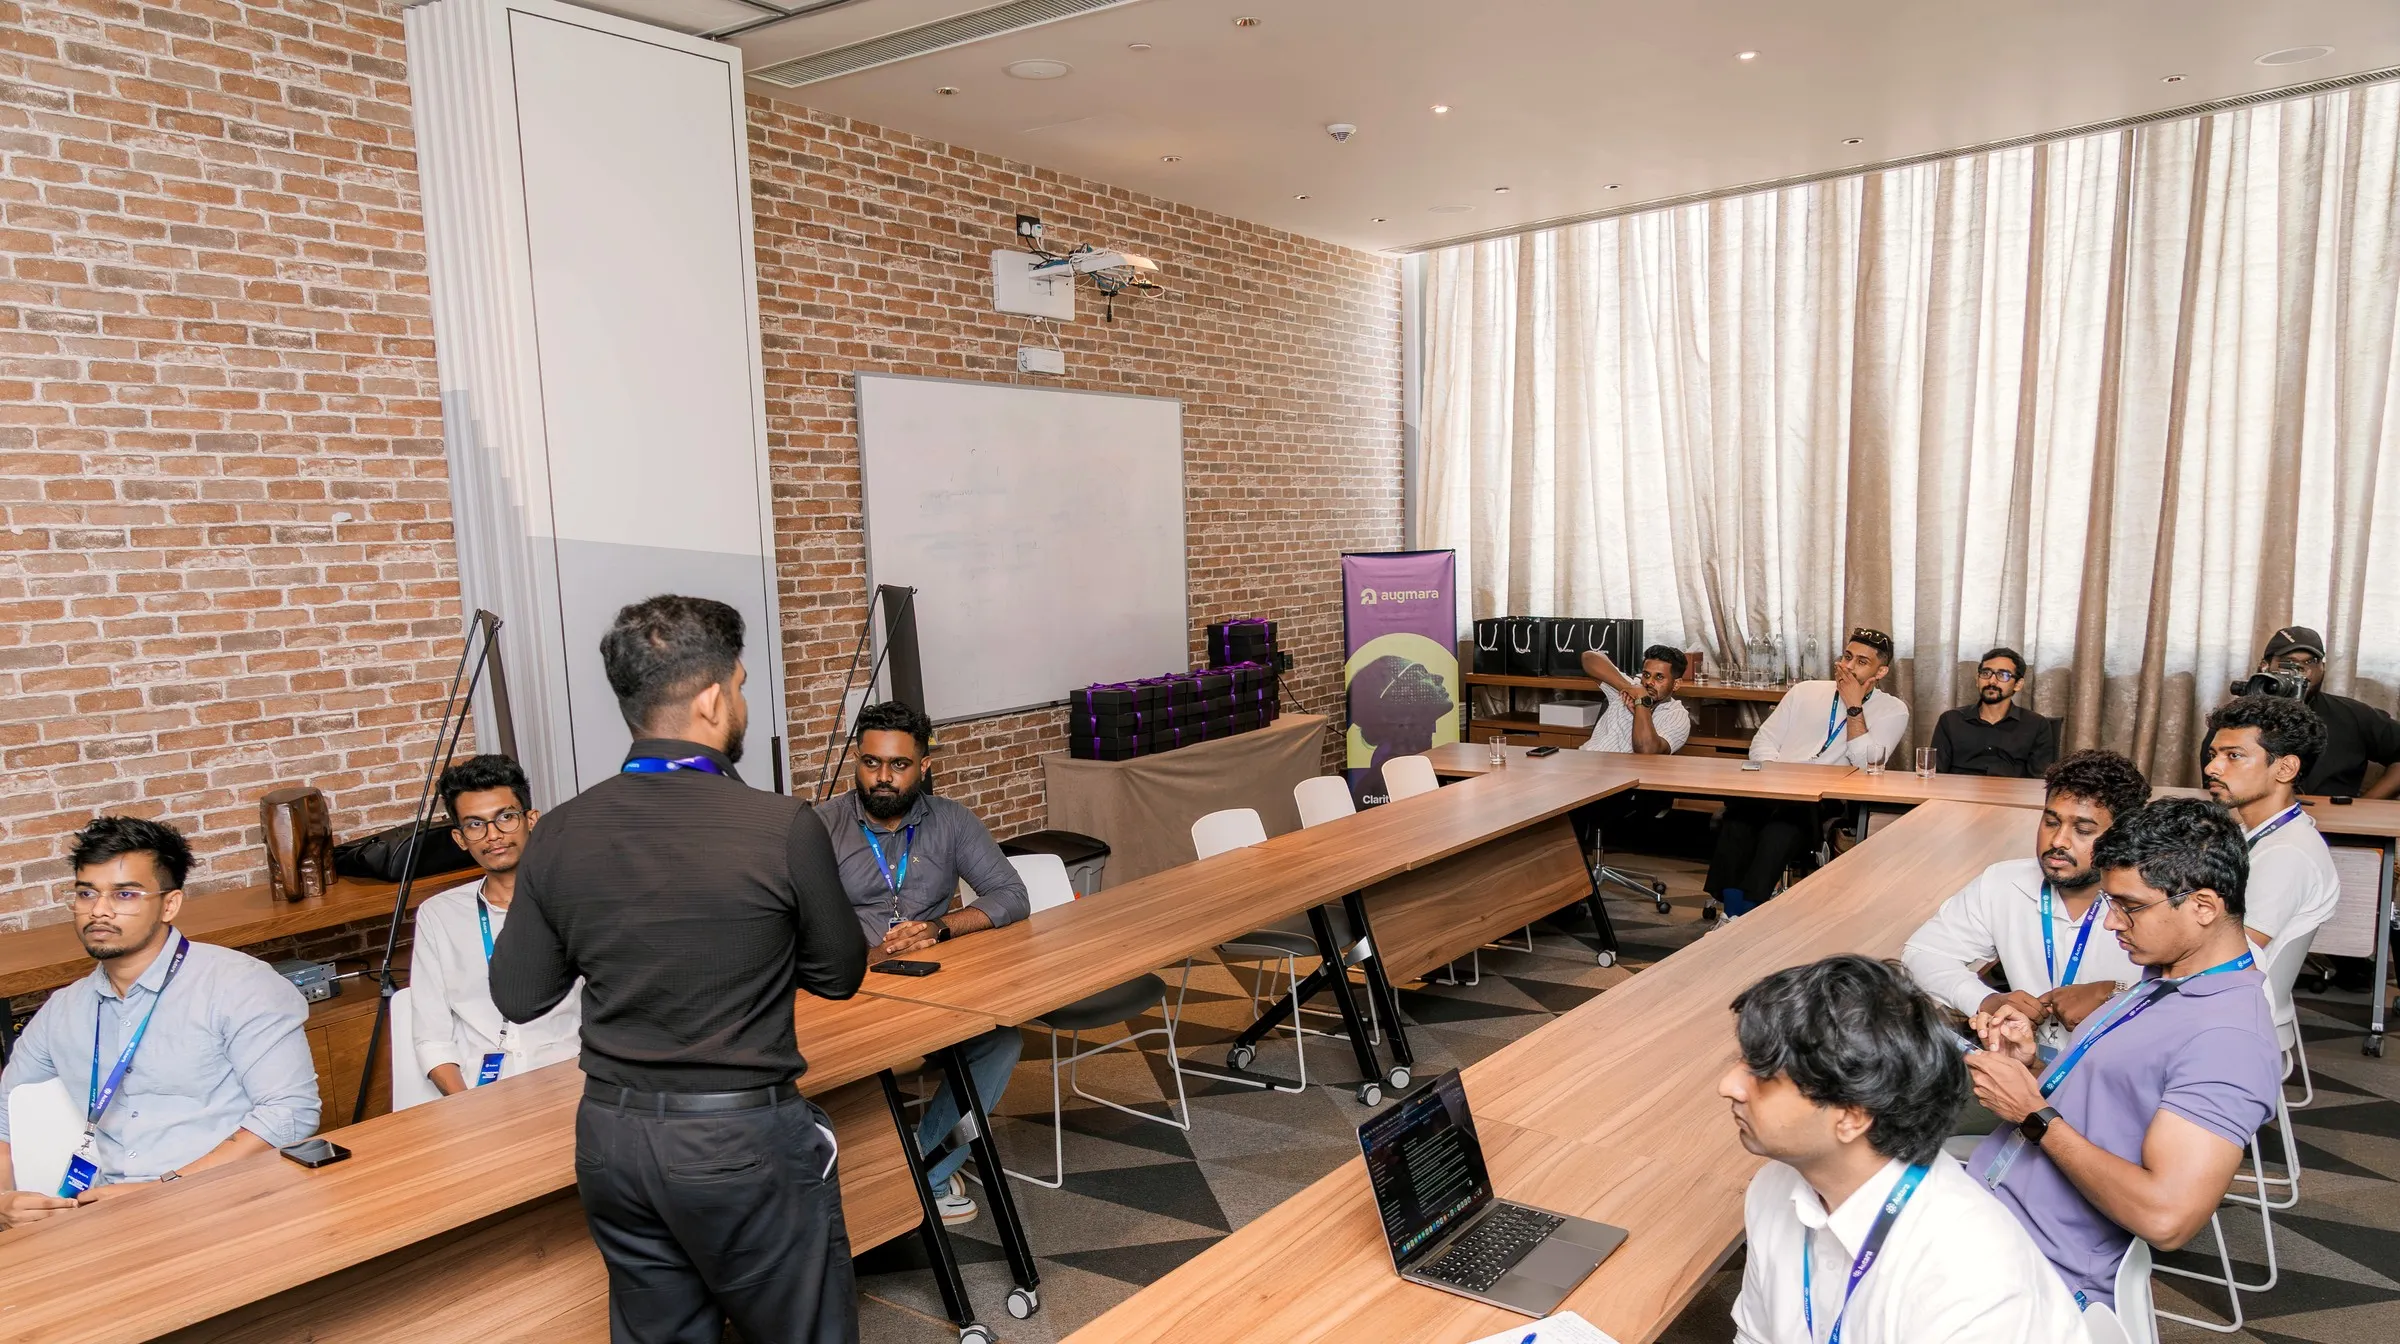
In the room
Workshops are where the real questions come out.
Past talks and events
Event names, dates and recordings will be listed here.
awaiting fact sheetWhat does Ravindu Fernando speak about?
Ravindu Fernando, a Colombo-based application security consultant, speaks on cloud web application and API protection (WAAP), API security, mobile app protection for banks, exposure management beyond CVSS scores, and how boards should measure application security maturity. Every talk draws on production programmes he has led.
Can a talk be tailored to our organisation?
Yes. Most sessions are adapted to the audience: a board wants risk and money, an engineering team wants patterns and pitfalls. Workshops can be run on your own architecture under an NDA, which turns the session into a light assessment.
Do you speak at events outside Sri Lanka?
Yes, in person across South Asia and the GCC where travel works, and remotely anywhere. Remote sessions work well for briefings and panels; workshops are better in the room.